
Report breaks down details behind malicious domains.
DomainTools today released its inaugural DomainTools Investigations Year in Review. The report examines domains used for malicious activities, including phishing, spam, and the distribution of malware.
DomainTools observed about 400,00 malicious domains in 2024. It broke down which domain registrars these names were registered with:
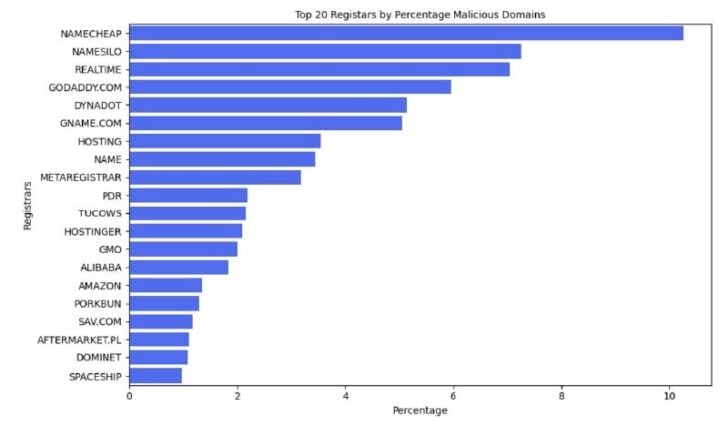
It’s worth noting that these are raw numbers, not percentages of the registrars’ total domain bases. One would expect larger registrars to show up on this list.
Similarly, CloudFlare, which provides free services to many domains, has the top nameserver used by malicious domains:

The report also noted that threat actors can leverage recently released top level domain names because some corporate security organizations use hard-coded TLD lists that might not include these domains.


Leave a Comment